

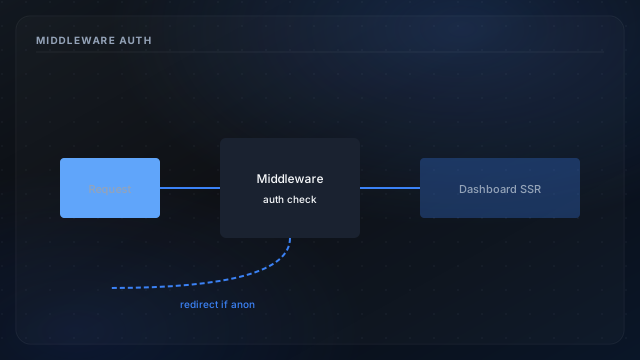
Authenticated dashboard pages must not rely on hidden UI alone. Astro middleware on Cloudflare can inspect cookies, validate JWT or session against Supabase, and redirect anonymous visitors to sign-in before expensive fetches run. The same layer protects API routes that mutate feed settings or trigger history inserts.
What to protect
- /dashboard/: settings, history, billing.
- POST API routes: feed updates, contact submissions.
- Leave public about and home unauthenticated unless A/B testing.
Session sources
Read HttpOnly cookies set during Supabase auth. Refresh tokens before SSR if your adapter supports it: details overlap cookie session lifecycle.
Edge considerations
Middleware runs at the edge, keep calls fast; cache public keys. Admin routes need role checks via group membership. Broader SSR context: Astro SSR.