

Edge-deployed Astro reads configuration from Cloudflare Workers environment at runtime. Service role keys and Stripe webhook secrets must never appear in client bundles or public GitHub repos. Separating **public** anon keys from **server-only** secrets mirrors relay hygiene in relay env vars.
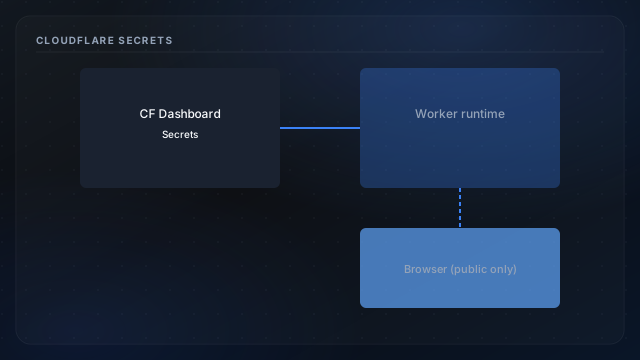
Variable classes
- PUBLIC_ prefix: safe for client islands if truly public.
- Server secrets. Supabase service role, Stripe secret, webhook signing.
- Per-environment: preview vs production values in separate namespaces.
Local development
Use .dev.vars gitignored locally; never commit. Rotate after laptop loss. Pair with middleware auth so mis-set keys fail closed on dashboard routes.
Deployment pipeline
CI sets secrets via wrangler or dashboard UI: document names in README without values. Related: Workers deployment and Tailwind v4 setup build env for CSS only.